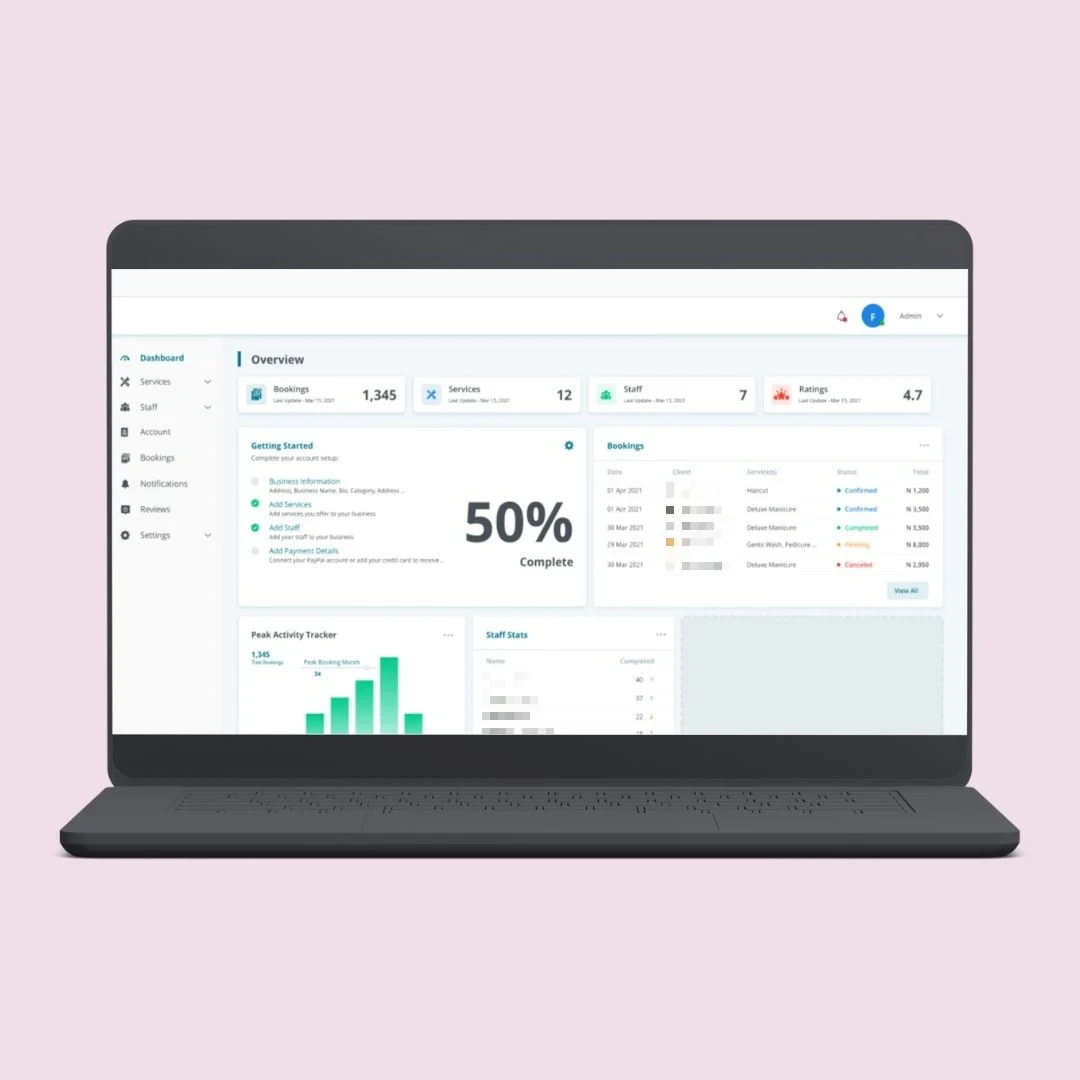
Role-Based Access
Separate patient, provider, prescriber and admin views, each with its own permissions.
Patient portals, provider portals, lab report delivery and clinical platforms, built around audit trails, access control and patient data protection from day one. Not retrofitted after a compliance review.
No audit trail. Weak access control. Patient data in places it shouldn't be. These three problems are behind most failed compliance reviews, and all three are decided when the system is designed, not when the auditor arrives.
We build custom healthcare systems designed around those requirements from the first day: every record access is logged, every role sees only what it should, and patient data is encrypted at rest and in transit.
Most healthcare teams come to us with one of these four problems.
No audit trail so nobody can show who opened a patient record, or when.
Weak access control with staff seeing far more patient data than their role needs.
Patient data in the wrong places in inboxes, spreadsheets and shared drives.
An audit or compliance deadline and a system that was never designed for one.
The technical safeguards auditors look for are part of the design, not an add-on.
Separate patient, provider, prescriber and admin views, each with its own permissions.
Every record access is logged: who, what and when.
Encryption at rest and in transit, with OAuth and multi-factor authentication.
Consent management and data retention controls built into the workflow.
OWASP-based penetration testing with a written report before launch.
We build for audit-readiness. Formal certification still requires an independent auditor.
Each system is custom built for your clinical workflow. No templates.
Patients book, reschedule, see results and message their provider securely.
Multi-role systems for providers, prescribers and admin staff, each with its own audit trail.
Records, notes and clinical workflows shaped around how your practice works.
Results delivered securely to patients and providers, with a record of every view.
Video consultations and messaging that keep patient data inside the system.
Billing, claims and insurance workflows, with practice and clinic management dashboards.
Every role gets its own screens and its own permissions, on the same secure backend.
Appointments, results, messages and documents, on web or mobile.
Clinical workflows, records and prescriptions with full audit logging.
Scheduling, billing, claims and result delivery in one place.
Adding audit logging and access control after a review is slower and costs more than building them in.
Start with the Architecture Blueprint: one week of work and a written build plan covering the data model, system architecture, scope, timeline and realistic cost. You can take it anywhere, including to another developer.Book A Call
Every project is scoped before it is quoted.
A written build plan: data model, architecture, scope, timeline and cost.
Agree who sees what, and what gets logged, before any screen is built.
Build with anonymised test data and connect your EHR, lab and pharmacy systems.
Security test, written report, then deploy to your own cloud account.
ASP.NET Core, .NET 8, SQL Server, React Native and Azure, with standard healthcare data exchange.
Healthcare systems, patient portals and lab report platforms are a core part of the projects we have delivered.
Discuss Your ProjectWe cover the technical half properly and tell you what sits outside software.
Full source code and IP, deployed to your own cloud. No vendor lock-in.
No subcontracting. NDA and BAA signed where required.
See how we have built booking, ordering and business platforms with role-based access.
The questions healthcare clients ask us first.
Send us your clinical workflow.
Book a Free ConsultationNo, and neither is any development company, because HIPAA certification doesn't work that way. There is no official certifying body for developers. What we do is build HIPAA-ready architecture: encryption, role-based access, full audit logging, consent controls and data retention policies. Formal compliance is assessed by an independent auditor, and we build so that assessment goes smoothly.
A week of work and a written build plan: data model, system architecture, scope, timeline and realistic cost. You can take it anywhere, including to another developer. Most people overestimate or underestimate their project by a wide margin. This removes the guessing before anyone commits to a build.
We build to the technical safeguards HIPAA requires, and offer a written readiness review showing where your system stands. Compliance also depends on your policies, training and business associate agreements, which sit outside software. We cover the technical half properly.
Yes. HL7 and FHIR data exchange for integrating with EHR systems, labs and pharmacies, scoped to your interface.
Yes, regularly. We assess it first and tell you plainly whether extending or replacing is the better decision for you, including when the answer is extend.
We work with anonymised or synthetic test data. We never require production patient records, and we sign an NDA and a BAA where required before any access.
Yes. Full source code and IP ownership, deployed to your own Azure account, so there is no vendor lock-in.
Compliance is half software and half process. Policies, staff training and business associate agreements matter as much as the system. We tell you clearly which parts we cover and which parts stay with you.
Need your current application checked first? See our VAPT security testing.
Need the clinical system behind the portal? See EHR and EMR software development and HL7 and FHIR integration.
Tell us the type of practice, the user roles and the core workflow. We'll scope it properly before we quote, and tell you plainly whether to extend what you have or replace it.